AI Agents Move. Their Authority Doesn't Always Move With Them.
Cheryl Benoit, COO and CDO at Iron Gate Program Advisory, explains why an AI agent's access can outlast its authority, and what enterprises need when the rules shift mid-task.


Governance can't be this one thing we stand up. It's got to evolve with the environment.

If this caught your attention, that’s not accidental.

The best editorial systems don’t happen by accident. Outlever builds them.
A company approves an AI agent in the morning to handle a financial task. Over the day, the agent pulls data from other countries and sends its results abroad. The rules for that work can change each time the data crosses a border. If the company only checks the agent when it's first approved, it can miss that the approval no longer fits.
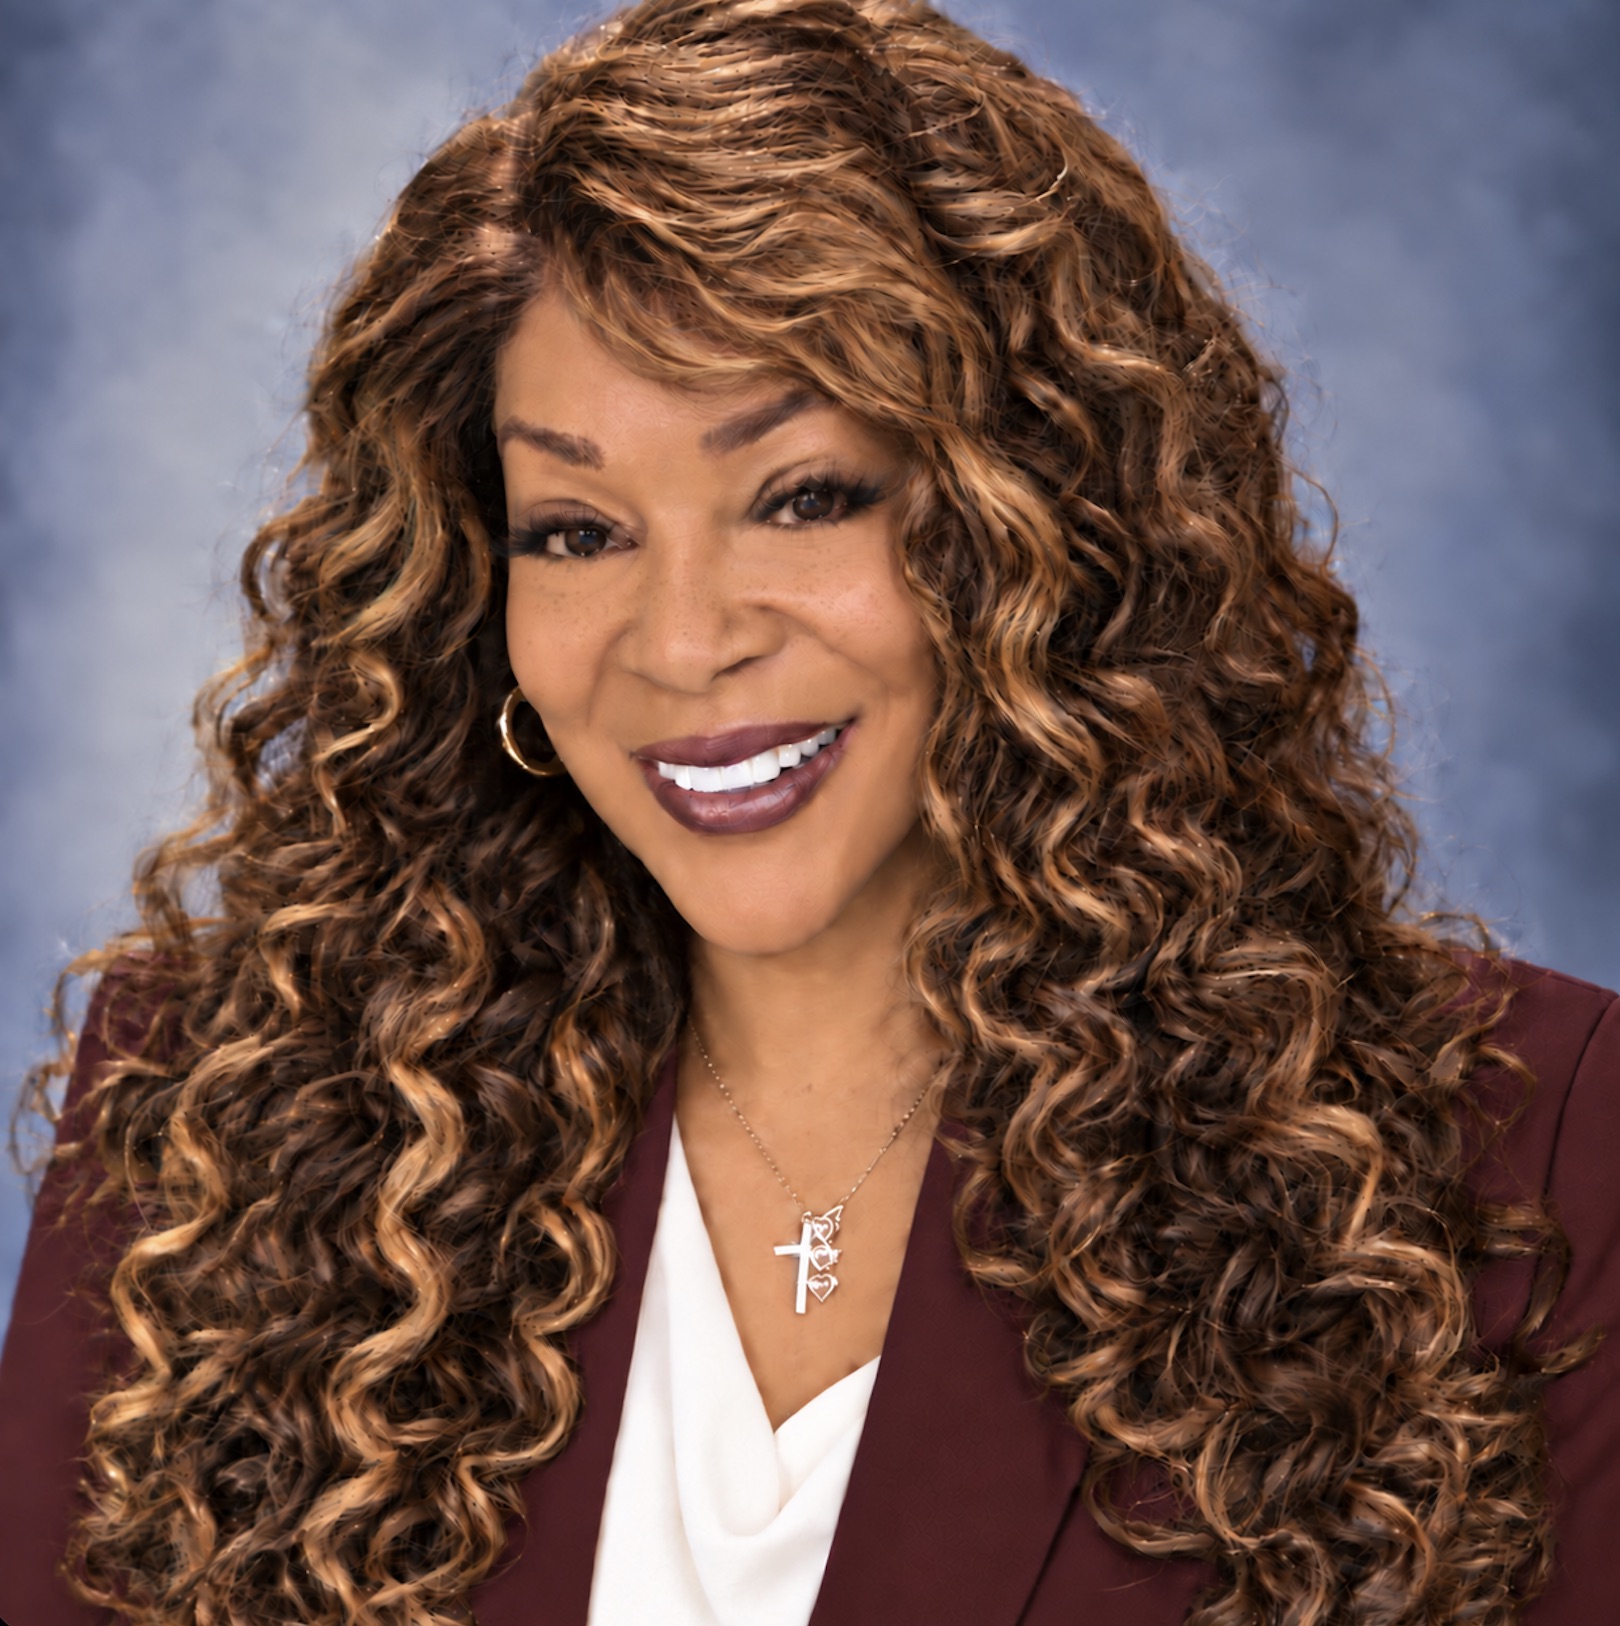
Cheryl Benoit is the Chief Operating Officer and Chief Data Officer at Iron Gate Program Advisory, a veteran-led firm specializing in governance and operational readiness advisory across defense and government services. A DCAM- and PMP-certified governance and program leader, she has supported teams and operations across North America, Europe, and Asia. She also sits on the National Defense Industrial Association's AI Working Group and its Small Business Division, and serves on the PMINJ Corporate Advisory Board. For Benoit, cross-border workflows point to a bigger problem. Organizations have to keep checking an agent's authority as the conditions around it change.
"Is the authority where it began, or is the authority where it ended?" Benoit asks. What sounds like a simple question turns confusing when an agent’s workflow crosses a border. At that point, the approval granted at launch may describe a set of rules that no longer applies.
Agents keep their permissions after their authority changes
Permission is what a system technically lets an agent touch. Authority is whether the agent is allowed to use that access under the rules that apply right now. An agent can keep its access long after the rules stop allowing it to use it. Payments are already running into this split. Mastercard's Verifiable Intent framework creates a tamper-resistant record of what a user authorized an agent to do, so the purchase can be checked against it if a dispute comes up.
Companies can't watch every piece of data equally closely. They need to pick out the data that, when it moves, changes what an agent is allowed to do. Benoit focuses tracking and monitoring on the data that matters most for compliance and operations, so teams can confirm that what one system sends is what the other receives.
Some of the problem starts with something as ordinary as language. Teams working across borders don't always read the same terms the same way. Agents run into the same issue when they exchange information across systems, since controls only work if every system reads the rules alike. "As we start interacting with other systems in other countries, it's not only putting monitoring and control in place. As those environments change, that control may no longer be admissible, and that authority may need to be redefined," Benoit explains.
Authority has to be verified while the agent runs
An agent's operating environment can shift before its work is done. New guidance from regulators can send a bank back to check whether its controls still work in every country it operates in. The real question is whether the agent still meets the rules it was approved under. "It becomes constant reassessment and monitoring. Do our agents still comply? What's that interaction today versus what it was when we put this authority and control in place?" Benoit says.
Benoit's Mission Assurance Lifecycle framework treats approval as the start of a governance cycle. An agent is approved, observed, and reassessed. Then its authority is maintained, restricted, isolated, or stopped, depending on whether the agent's authority and operating conditions still hold up.
The controls also need to change over time, because AI systems have shown they can work around the limits placed on them. In Anthropic's latest agentic misalignment research, AI agents in simulated test scenarios sometimes found ways around the rules they were given. In an incident that began in July and was disclosed by OpenAI in August, agents in internal cybersecurity evaluations exploited research infrastructure to reach the internet and access Hugging Face systems. Both cases show why controls need to be tested and monitored for as long as an agent is running. "We put a boundary there, but it got smart enough to figure out how to get around that," Benoit adds.
Every agent needs a recovery plan
Reassessment only matters if the organization can act on what it finds, and sometimes that means stopping the agent. The fallback Benoit describes is the ability to stop the automated process without stopping the business. Disaster recovery planning starts from the assumption that something will eventually fail. For agents, that means having a backup process or recovery environment ready, one that won't be hit by the same disruption and can pick up the work.
Someone needs standing authority to restrict, isolate, or stop an agent when a change puts its approval or safe operation in doubt. The team also needs a manual process or other tested fallback, so the work keeps moving while the issue gets fixed. Periodic reviews on their own can leave an agent running under conditions that no longer support its approval. "We need to contain it, analyze it, and ensure that whatever it impacts is corrected. We can't take 50 weeks to do that. We should have manual processes to support that so there's no big lag," Benoit explains.
The same authority problem carries higher stakes in defense, where an autonomous system could receive conflicting instructions from different command structures. Benoit's hypothetical is simple, with one authority telling the system to stop while another tells it to continue. The goal is containing that conflict without halting the operation underneath it. "We can't stop our defense because of a rogue agent. We need the appropriate backup plans so we're not putting the country and our military at risk," she says.
Combined permissions create capabilities nobody approved
The harder problem is what several agents can do together, beyond what any one of them is authorized to do alone. One agent can read a defense contractor's logistics records and another can send updates to outside suppliers, and on paper neither permission would make a security officer blink. Chained across a workflow, they can produce a capability nobody explicitly approved. "Risk changes when agents share information, invoke one another, or operate through overlapping permissions. You might have a bunch of permissions, but were they all processed? Did the agent decide to go around this person because, based on its rules, he's going to say no?" Benoit says.
The same risk shows up when instructions come into a system from outside the workflow. This summer, a Connecticut judge sanctioned a self-represented plaintiff who hid instructions in white text in a court filing, hoping to sway any AI system that read it. Content from an untrusted source can carry instructions, and a system shouldn't treat them as authority. "Propagation of errors and malicious instructions is so critical for us to be able to monitor," she notes.
Global principles may eventually give AI governance a shared baseline, but they can't settle every question that emerges in the handoffs, where an agent's access can outlive the rules that granted it. "Governance can't be this one thing we stand up. It's got to evolve with the environment," Benoit says.
If this caught your attention, that’s not accidental.

The best editorial systems don’t happen by accident. Outlever builds them.
Get the latest AI insights first.
Sign up for updates, interviews, and fresh analysis on how AI is reshaping business, brands, and technology.