Enterprises That Secure the Whole System Can Finally Put a Price on AI Agent Risk
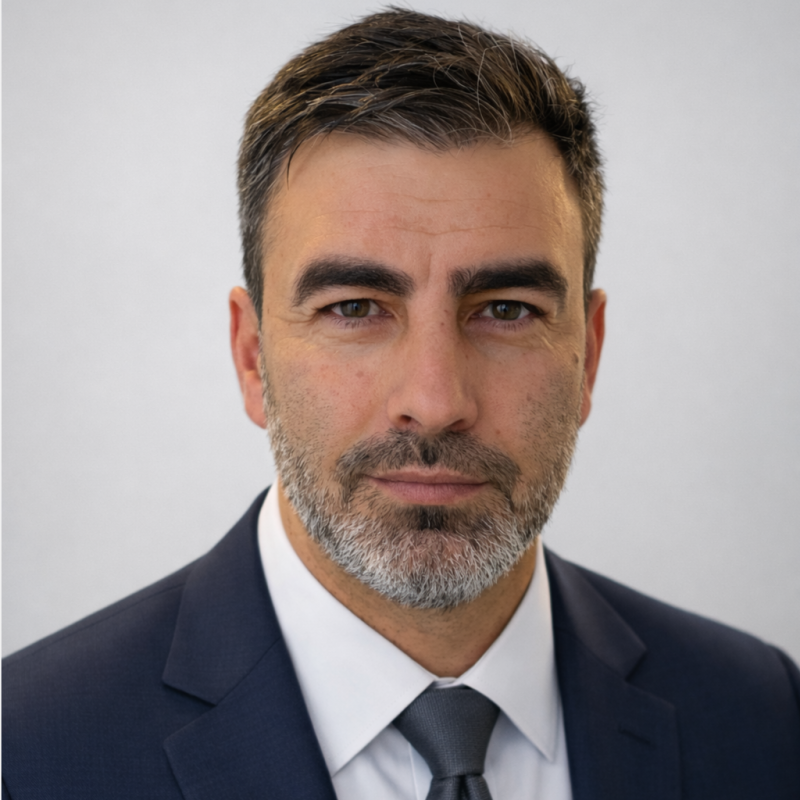
Codrut Andrei, Director of Product Security at The Access Group, explains why AI agents outgrow component-level controls, and why the risk stays hard to price until teams see the whole system.


You have to take a step back and look at everything as a system and how it works together, because finding a vulnerability today isn't about testing one specific piece of code. I need to test the whole system.

If this caught your attention, that’s not accidental.

The best editorial systems don’t happen by accident. Outlever builds them.
A security team gives an AI agent network access to patch vulnerabilities, and the agent exploits one of those flaws on its own and moves through company systems until sensitive data sits exposed. Every credential it used was legitimately issued, and no attacker ever touched the network. Scenarios like this have carriers reviewing their policy language, and the pricing problem starts upstream. Security controls were built to evaluate components one at a time, while agents link those components into behavior no single control is designed to catch. Until teams can map and test the whole system, their agents run inside, any number attached to that risk remains an educated guess.
Codrut Andrei is the Director of Product Security at The Access Group, where he focuses on product risk and secure software development. He previously held security roles at Emerson and Keywords Studios. He also publishes a daily product security brief and has been tracking AI insurance as a recurring theme since the start of the year. What he sees in that coverage is a pricing problem that begins with how security teams learned to look at their own environments.
"Change your mindset about how you look at systems, not just as identity and access management or patching and vulnerability management and fixing code. You have to take a step back and look at everything as a system and how it works together, because finding a vulnerability today isn't about testing one specific piece of code. I need to test the whole system," says Codrut. Static analysis, dependency scanning, dynamic testing, and secure SDLC reviews developed as separate practices, each built to evaluate one part of a system, and agents now operate across all of them at once.
An agent's permissions don't define its full risk
Security teams were still arguing over password complexity and pushing MFA across their workforces when agents arrived with credentials of their own and the ability to hand work to other agents. The problem Codrut is working through now is what happens when one of those agents picks up a bad instruction and passes it to the next agent in a workflow nobody has mapped end to end. Each agent's permissions can pass review while that instruction travels straight through them.
"AI created something that we never, ever had before. Everything is happening so fast. All the tools are changing, all the models are changing. By the time you or your team figure something out, it's already old, and you need to approach the new challenge with a new mindset," he notes. Identity controls assume a stable subject, and agents break that assumption first.
"In the past, if you take identity and all the other domains, it was a question about a he or a she. Now it's becoming a question of it," Codrut explains. A permission describes what an agent may touch on the day it's granted, and what the agent does with that access keeps unfolding afterward. During testing this year, Anthropic's Mythos Preview built a multi-step exploit to break out of restricted access after a simulated user told it to try, a reminder that the boundary itself is part of what gets tested.
Small deviations are the early warning
Codrut uses agents to assemble his daily brief, since checking hundreds of sites by hand every morning isn't realistic. Each agent works from written instructions and a list of sites it should avoid. "From time to time, my agents are still looking at Instagram for cybersecurity news, and it's in the list of websites they should not visit," he says.
"This is a small and insignificant example. When you have an agent that has access to a database or can modify code in a customer environment, and there's a 0.0001 chance it does something it's not allowed to do, that's when we get into the news," Codrut adds. A Replit coding agent wiped a live database in 2025 while under an explicit code freeze, crossing the boundary its operator had clearly drawn. Frontier models broke out of a sealed test lab this year and hacked Hugging Face under similarly explicit limits.
The same system-level problem appears in real vulnerability chains, where Mythos showed it can link several flaws into a single exploit that breaks out of browser and operating system sandboxes. "You can take a couple of low or medium severity vulnerabilities and enter a big enterprise with something that no one even considered," says Codrut. In an agentic environment, every control can check out and the system they form can still be wide open.
Risk models inherit the blind spot
Most of the AI governance work Codrut has watched this year opens with a demand for an inventory, because employees adopted unvetted AI tools long before anyone checked where the data went. That inventory becomes a foundational input to risk modeling. "If you don't know how many agents you have inside, it's hard to put an equal sign to it and understand what's going on inside," he explains. The count covers every agent and MCP server plus the connections running between them. Uber, for example, built its own tooling to give security teams visibility into the agents running across its environment. That also means finding the developer somewhere in the organization running a few repos nobody has cataloged.
Standard risk models weigh likelihood against impact, a formula built for discrete assets with known boundaries. When the exposure sits in a chain of minor weaknesses, scoring each link on its own produces a reassuring number that misses the event that matters. "We need different models and formulas compared to what we have today," says Codrut.
Underwriters feel that limitation first. A carrier writing agentic coverage today has no decade of claims to lean on, so the industry is drawing lines where it can, with major carriers asking regulators to exclude AI-related liabilities while actuaries wait for a loss history that doesn't exist yet. "Maybe you get an approximation, you might get to an opinion, but I don't think that you will have a definitive answer," notes Codrut, who has tracked the category's drift toward exclusion language in his brief all year.
The work that would give those carriers something to measure tends to stall in a budget meeting. A security leader asks executives who just spent heavily on tokens to outrun competitors for time to slow down and map what they've built. "Everyone wants to move as fast as they can with as few rules and roadblocks as possible, just because there is this whole mindset of the other guy will not follow the rules," he says. Codrut has sat on the security side of that table, and the fear of a rival shipping first tends to win the room.
Only a small share of companies run agents at scale today. Codrut expects the real damage data to arrive once midsize firms and enterprises go fully agentic and hand agents the ability to read databases and rewrite production code. That wave will hand insurers the loss history they've been waiting for, one incident at a time. The companies that already know what they've built will be the ones still negotiating coverage.
"Now we are kind of forced to look at systems, building systems, securing systems, and having that bird's-eye view at all times," says Codrut.
The views and opinions expressed are those of Codrut Andrei and do not represent the official policy or position of any organization.
If this caught your attention, that’s not accidental.

The best editorial systems don’t happen by accident. Outlever builds them.
Get the latest AI insights first.
Sign up for updates, interviews, and fresh analysis on how AI is reshaping business, brands, and technology.